When businesses talk about cybersecurity, the conversation often starts with antivirus software, passwords, firewalls or security tools.
But there is something underneath all of them that is easy to overlook:
The network itself.
A business can have security software installed on every computer and still have a weak security architecture if its underlying infrastructure is poorly designed.
Network security is not simply about adding security products. It starts with understanding how devices connect, how data moves, who can access what, and what happens when something goes wrong.
A well-designed network creates the foundation on which other security controls can operate.
Security Begins With Understanding the Network
Modern businesses rarely have just a few computers connected to a router. A typical business network may include:
Each device introduces connectivity requirements and potentially another path into the network. The first step toward better security is therefore understanding the environment—the same discipline behind avoiding the pitfalls we describe in 5 Common Networking Mistakes Growing Businesses Make.
You cannot properly secure a network you have not properly designed or documented.
One Network Does Not Have to Mean One Flat Network
One of the common approaches in smaller businesses is to connect everything to the same network. Employees, guests, CCTV cameras, printers and other devices may all communicate within the same environment. This may be convenient, but it can create unnecessary exposure.
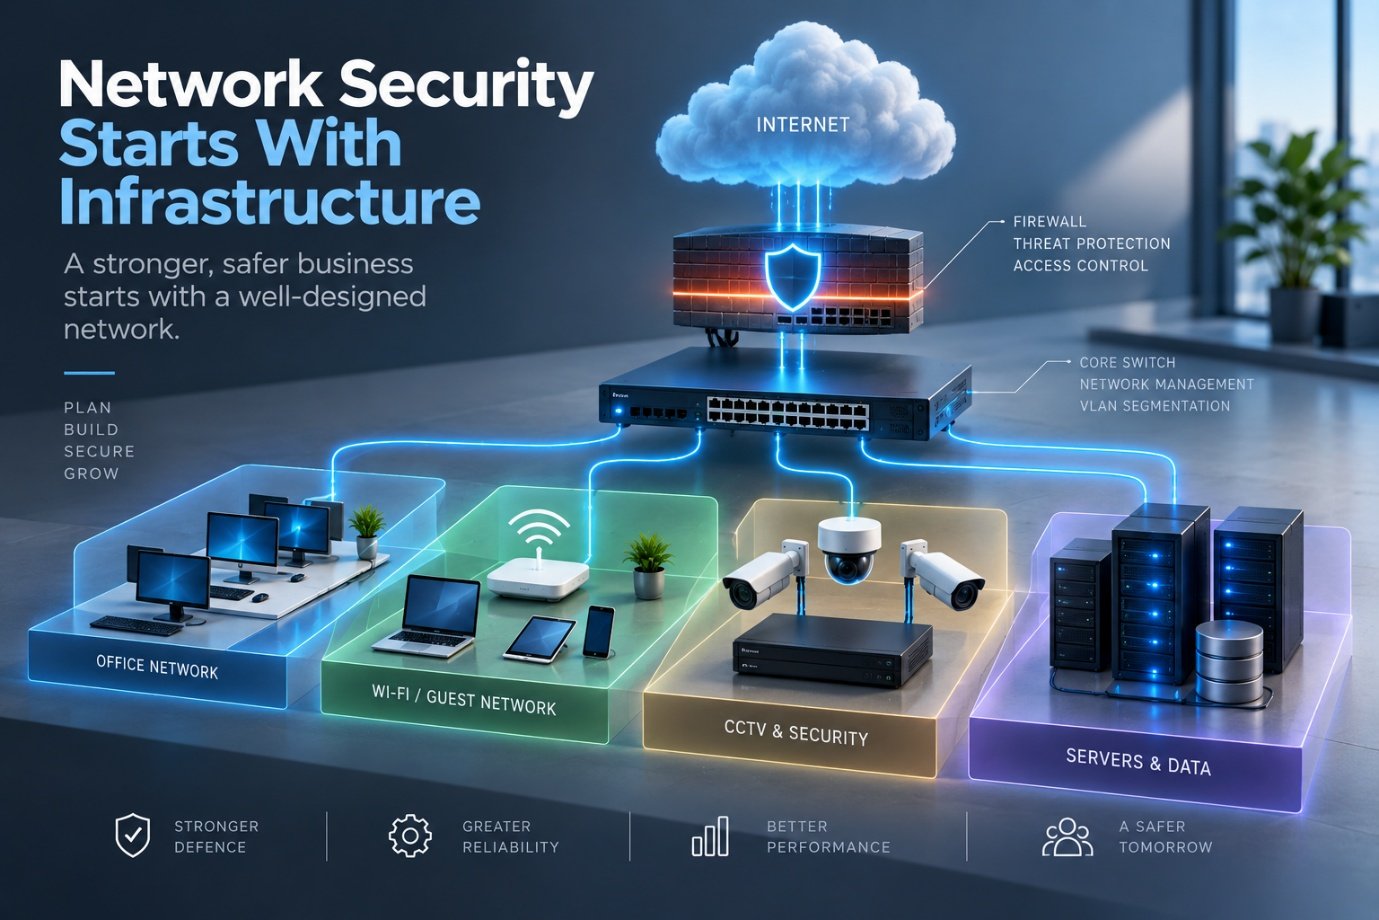
Network segmentation can divide a network into separate logical or physical zones, limiting communication between them. CISA identifies segmentation as a technique that can provide additional security and control by separating networks and restricting access between them. For example, a business could have separate network segments for:
- Employee computers, laptops and business applicationsCorporate Network
- Visitors and customers who need internet access but not internal systemsGuest Wi-Fi
- Cameras, NVRs and related surveillance equipmentCCTV Network
- Smart devices and other connected equipmentIoT Network
- Critical servers and infrastructureServer Network
- Network equipment and administrative interfacesManagement Network
The exact architecture depends on the organisation, but the principle is simple:
Not every device needs to communicate with every other device.
VLANs Are More Than a Networking Feature
VLANs, or Virtual Local Area Networks, are often discussed as a way to organise network traffic. They can also play an important role in network architecture and security. A VLAN allows a physical network to be divided into logical networks, helping separate different categories of devices and control how they communicate. For example:
- Employees and business computersVLAN 10 — Office
- Visitors and temporary usersVLAN 20 — Guest Wi-Fi
- Cameras and recording systemsVLAN 30 — CCTV
- Business-critical systemsVLAN 40 — Servers
- Network administrationVLAN 50 — Management
However, simply creating VLANs does not automatically make a network secure. The traffic between those segments still needs to be properly controlled through firewalls, access-control rules and other security mechanisms. Security depends on the architecture and configuration, not simply the presence of a VLAN.
Your CCTV Network Is Part of Your Security Architecture
CCTV is often treated as a completely separate project. The cameras are purchased, installed and connected to an NVR, and the job is considered complete. But modern IP CCTV is fundamentally a networked system, exactly as we explored in Modern CCTV Is More Than a Security Camera. A typical deployment involves:
This means CCTV infrastructure needs to be considered alongside the wider network—and many of the same planning gaps we cover in CCTV Design Mistakes That Can Cost Businesses More Than the Cameras trace back to networking. Questions should include:
- Should cameras share the corporate network?
- Should CCTV traffic be placed on a separate VLAN?
- How much bandwidth will the cameras require?
- Where is the recording stored?
- Who can access the cameras?
- How is remote access secured?
- What happens if the network fails?
- How long must recordings be retained?
A camera may be physically located on a wall, but from an IT perspective it is another connected device.
Firewalls Are Only One Layer
A firewall is an important component of network security, but it should not be viewed as the entire security strategy. A properly designed network can use multiple layers:
This layered approach is often referred to as defence in depth. CISA guidance recommends using measures such as firewalls, access controls, segmentation and DMZs as part of a broader layered security architecture rather than relying on a single control. If one security layer fails, other layers can still provide additional protection.
Access Should Be Based on Need
Another important principle is controlling who—and what—can access different parts of the network. An employee's laptop may need access to business applications. A guest's smartphone probably needs internet access. A CCTV camera needs to communicate with its recording infrastructure. A printer may need to communicate with employee devices.
But that does not mean all of these devices should have unrestricted access to everything else. Network rules should be designed around business requirements and least-privilege principles. This can reduce unnecessary communication paths and limit the potential impact if a device or account is compromised.
Wi-Fi Is Part of the Security Architecture
Wi-Fi is sometimes treated simply as a convenience. In reality, it is one of the most visible entry points into a business network. A good business Wi-Fi design should consider:
Guest Wi-Fi is a particularly important example. Visitors should be able to access the internet without automatically gaining access to internal business systems. This is where good network design becomes more important than simply purchasing a more powerful wireless router.
Network Security Also Depends on Physical Infrastructure
Cybersecurity conversations can become so focused on software that physical infrastructure gets forgotten. But consider what happens if:
These may not be conventional cyberattacks, but they can still affect availability and business operations. Network security therefore overlaps with network reliability and resilience—the same foundations laid out in How to Build a Reliable IT Network for a Growing Business and Scalable IT Infrastructure: Building for Growth Without Overbuilding. Good infrastructure planning includes:
Security is not only about preventing unauthorised access. It is also about keeping important systems available and controllable.
Network Management Matters
A network that nobody monitors is difficult to secure effectively. Businesses should have visibility into their infrastructure. Depending on the size and complexity of the environment, this can include monitoring:
Documentation is equally important. A business should know:
- What devices do we have?
- Where are they connected?
- Which systems depend on them?
- Who manages them?
- What happens if one fails?
As businesses grow, undocumented networks can become increasingly difficult to manage.
Remote Access Needs to Be Designed Carefully
Remote working and cloud applications have changed how employees access business systems. Remote access can be useful, but it should not mean exposing internal infrastructure unnecessarily. Remote-access architecture should consider:
CISA guidance specifically recommends restricting remote access, using strong authentication and cryptography, and separating management access from normal production traffic where appropriate. The objective is not to make remote work difficult. It is to make remote access controlled and intentional.
What Happens When a Device Is Compromised?
Good infrastructure planning also asks an uncomfortable but important question: what happens if one device is compromised?
Imagine an employee laptop becomes infected. If every device and system sits on one flat network, the compromised machine may have unnecessary connectivity to many other systems. A segmented architecture can reduce those pathways. Similarly, if a connected device such as a camera or IoT device is compromised, appropriate network controls can help limit what it can communicate with. This is one of the reasons infrastructure design matters so much.
Security is not only about keeping threats out.
It is also about limiting how far a problem can travel.
The Connection Between Networking, CCTV and IT
This is where networking becomes particularly interesting for modern businesses. Consider a hotel. It may have:
These may appear to be separate technologies. But underneath them is a common infrastructure:
The network becomes the platform connecting the different parts of the business—the same connective role we describe in APIs: The Missing Link Between Your Business Applications. That is why networking should not be treated as simply "installing Wi-Fi."
Security Should Be Designed Before the Network Is Installed
One of the biggest opportunities businesses have is to consider security during infrastructure design rather than after installation. Instead of:
a better approach is:
This can prevent expensive redesigns later. It can also make the environment easier to manage as the business grows.
A Practical Network Security Checklist
Before deploying or upgrading a business network, consider:
Create an inventory of computers, servers, cameras, IoT devices and network equipment.
Identify which systems contain sensitive or business-critical information.
Separate users, guests, CCTV, servers and other device groups where appropriate.
Define which networks and devices actually need to communicate.
Avoid exposing internal systems unnecessarily.
Management interfaces should not be openly accessible from untrusted networks.
Use appropriate racks, cabling, power protection and environmental controls.
Know when important infrastructure or services become unavailable or behave unexpectedly.
Network diagrams, IP addressing, VLANs, equipment and access rules should be documented.
Today's network should not become tomorrow's bottleneck.
Network Security Is a Business Infrastructure Decision
Cybersecurity is often presented as a technology problem. But the foundation is much broader. It involves:
Each layer depends on the others. A firewall cannot compensate for a badly designed network. A secure Wi-Fi password cannot compensate for uncontrolled access between network segments. A CCTV camera cannot provide reliable surveillance if the network and storage infrastructure are poorly designed. And security software cannot solve every infrastructure problem—the same reason we caution against equating new software with real progress in Digital Transformation Isn't About Buying More Software. Getting the sequence right also matters for automation: as we explore in The AI Journey: What Businesses Should Automate First, systems built on an undocumented, unsegmented network are a poor foundation for automation and AI.
The strongest security architecture is built into the way the business operates.
The TRUIX Perspective
At TRUIX, we believe networking should be designed as part of the wider technology environment—not as an isolated IT installation. That means looking at the complete picture:
The objective is not simply to install more equipment. It is to build an infrastructure that is:
- Secure
- Reliable
- Scalable
- Manageable
- Resilient
- Appropriate for the business
Because when the infrastructure is designed properly, security becomes part of the architecture rather than an afterthought.
Design it right, and everything else gets stronger.
Related Reading
- Cloud vs On-Premise Infrastructure: What Should Your Business Choose?
- Why Your Business Network Is the Backbone of Digital Transformation
- Common CCTV Installation Mistakes Businesses Make
- AI Agents vs Traditional Automation: What's the Difference?
- How to Build a Reliable IT Network for a Growing Business
- 5 Common Networking Mistakes Growing Businesses Make
- Scalable IT Infrastructure: Building for Growth Without Overbuilding
- Modern CCTV Is More Than a Security Camera
- CCTV Design Mistakes That Can Cost Businesses More Than the Cameras
- APIs: The Missing Link Between Your Business Applications
- Digital Transformation Isn't About Buying More Software
- The AI Journey: What Businesses Should Automate First
- Networking Solutions